AI · SEMICONDUCTOR · FACT CHECK
 SKD WIRE
Mostly True
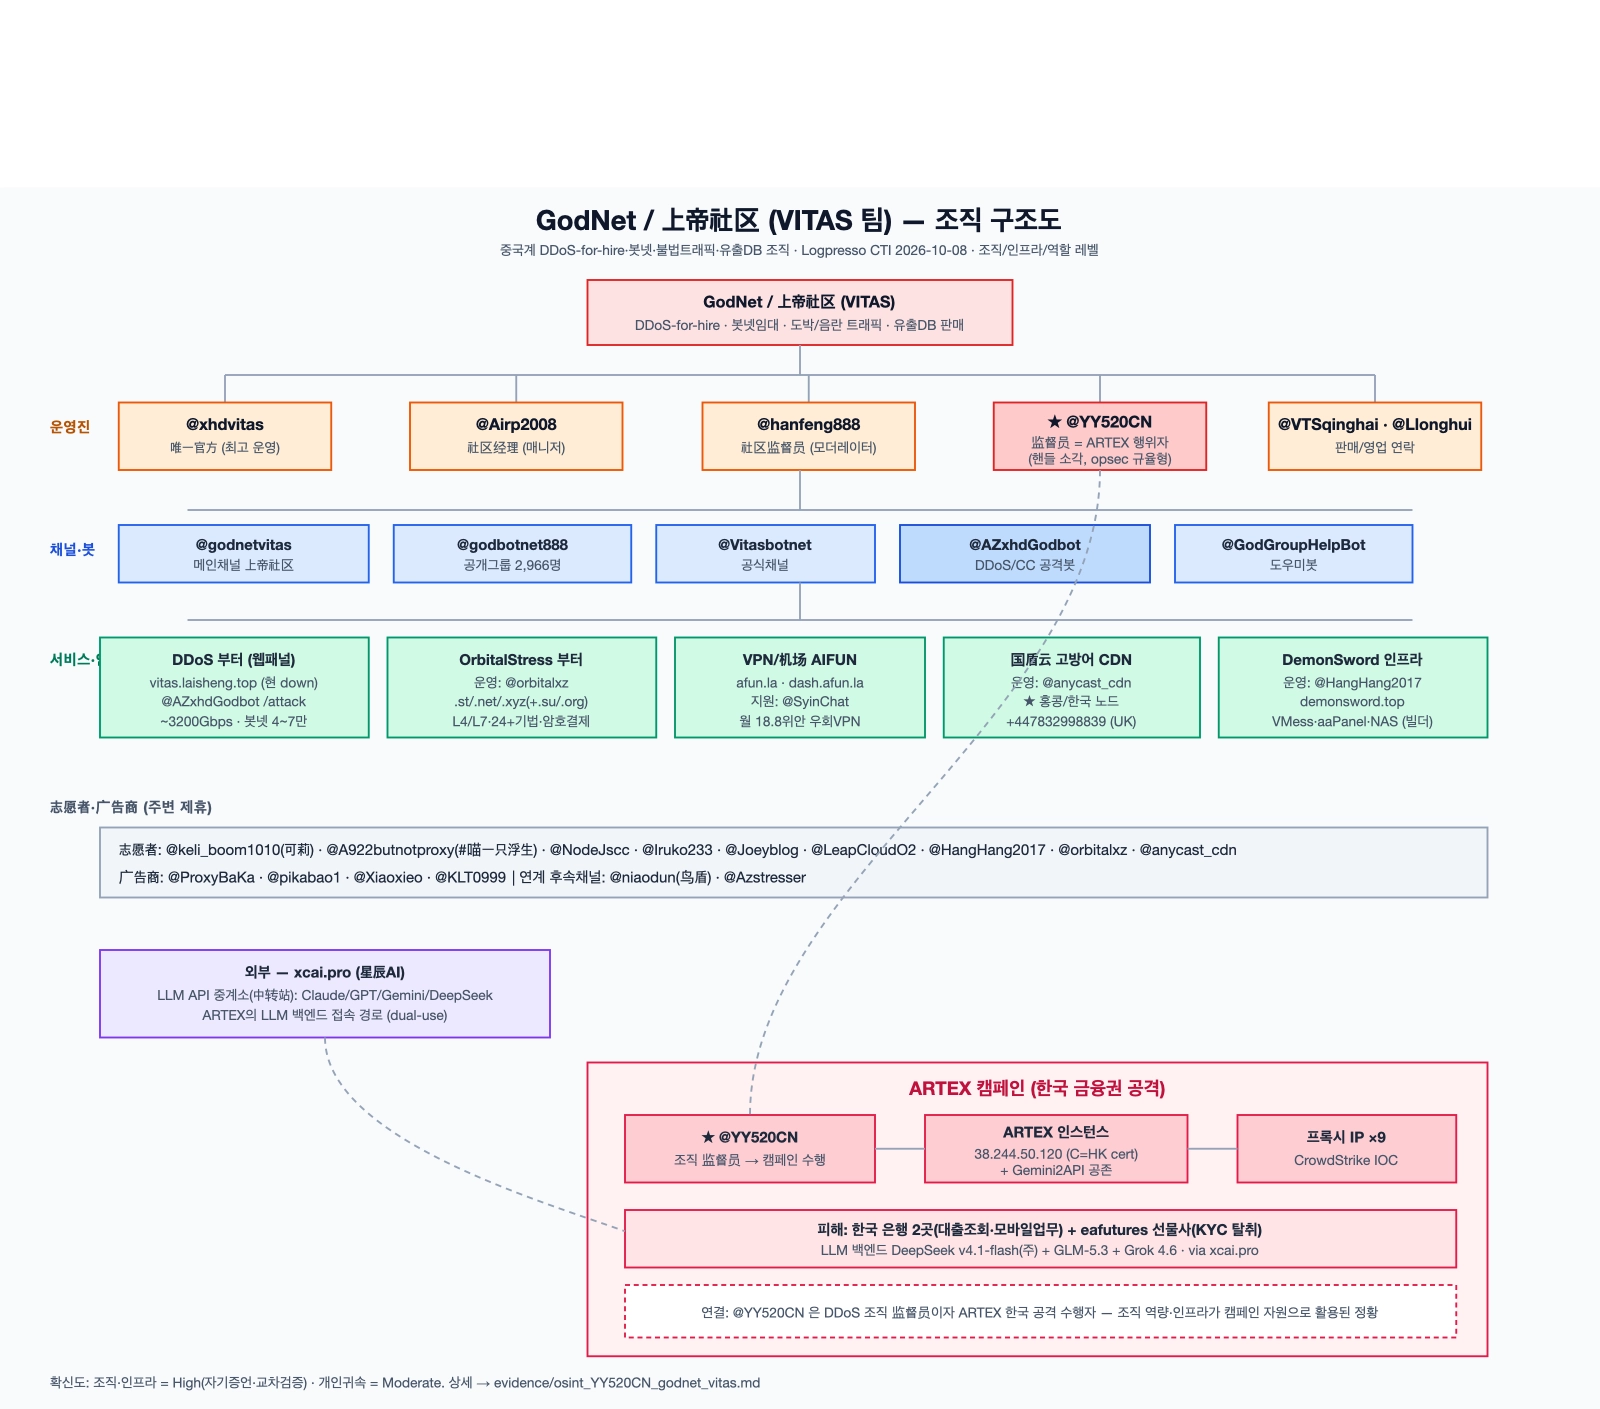
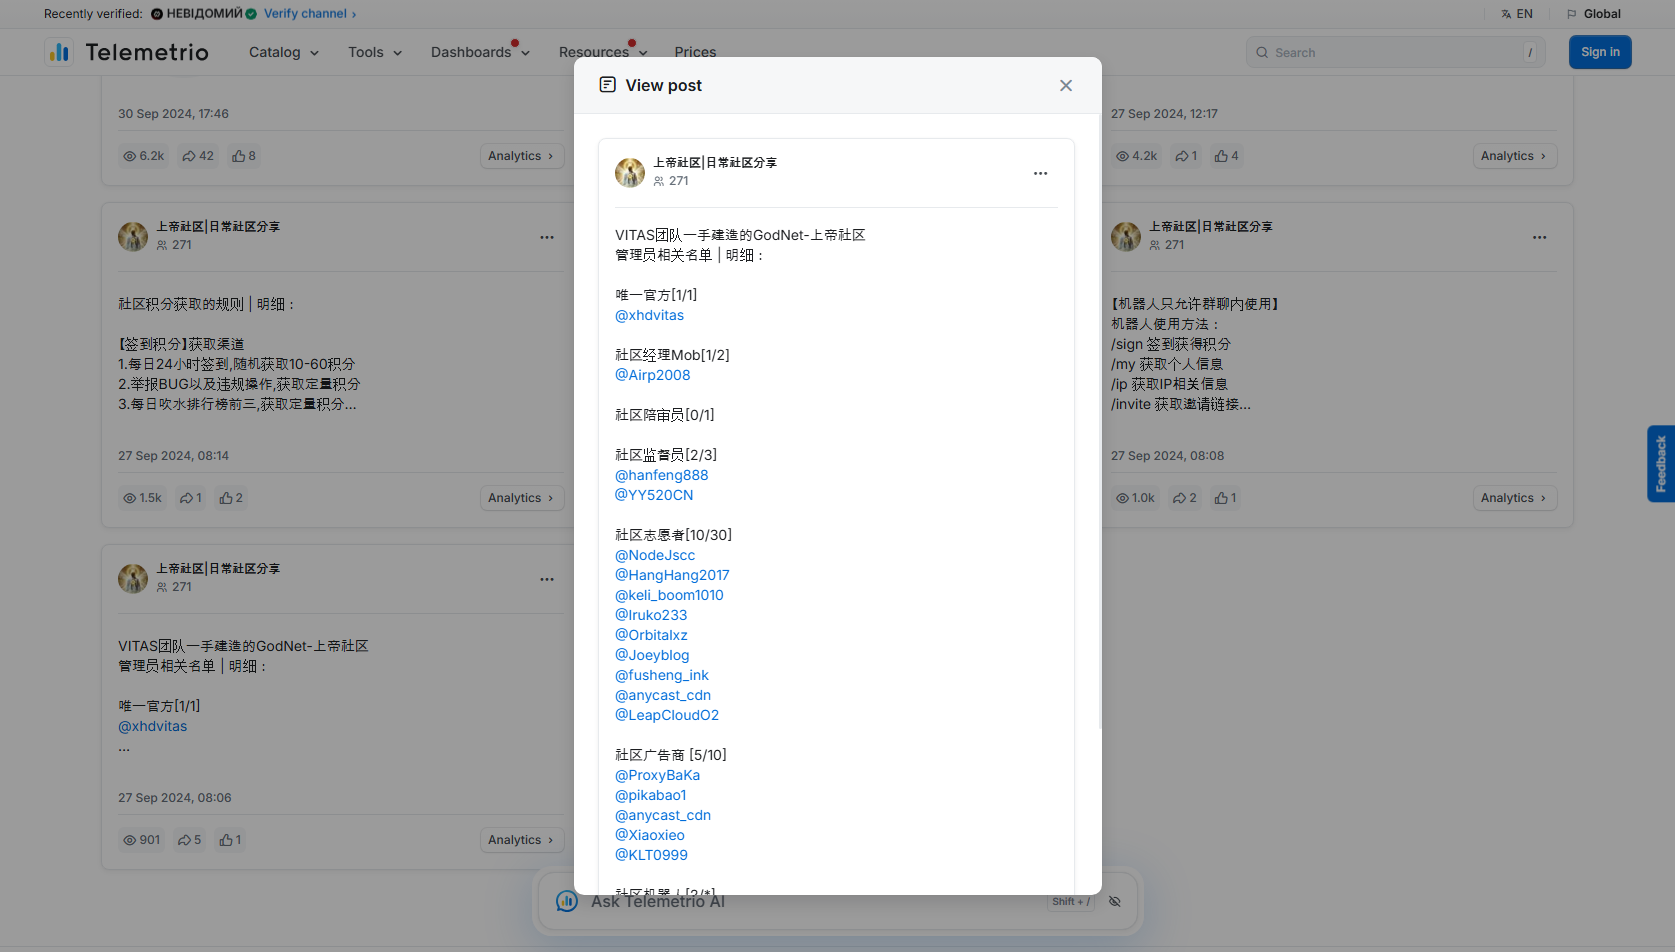
An OSINT analysis published by Logpresso indicates that attackers who used AI to penetrate South Korean financial institutions show traces of links to a Chinese distributed denial-of-service (DDoS) group, with the findings drawn from a review of 12 primary sources.
According to the Logpresso OSINT analysis, the attackers leveraged AI tools in their intrusion into Korean financial institutions, and indicators gathered during the investigation suggest a connection to a DDoS group operating out of China. The analysis includes structural diagrams and telemetry data supporting the assessment of the attack chain.
The findings place the case in a broader pattern of cross-border cyber operations targeting the APAC region, where threat actors increasingly combine AI-assisted techniques with established attack infrastructure. The specific identities of the targeted institutions and the full extent of the damage were not detailed in the published analysis.
While the analysis points to involvement by a Chinese DDoS organization, the report treats the connection as indicative rather than definitive, leaving open questions about whether the group acted directly or supplied infrastructure to other actors. The determination rests on the telemetry and structural evidence cited in the report.
South Korean authorities, including the National Intelligence Service, have not been cited in the analysis as having issued an official attribution, and no independent government confirmation is reflected in the published material.
The evidence supports the core claim while leaving some attribution questions open — the findings are Mostly True.
Verdict: Mostly True