AI · SEMICONDUCTOR · FACT CHECK
 SKD WIRE
Mostly True
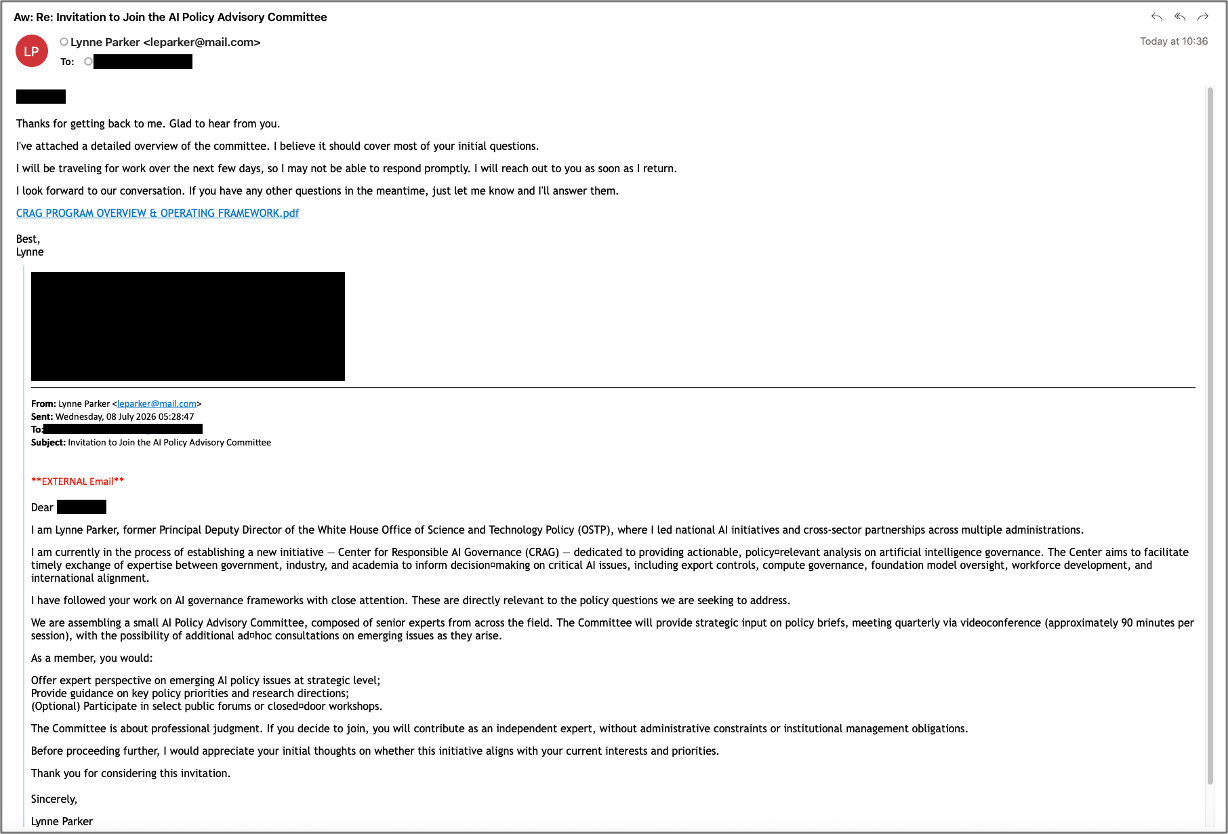
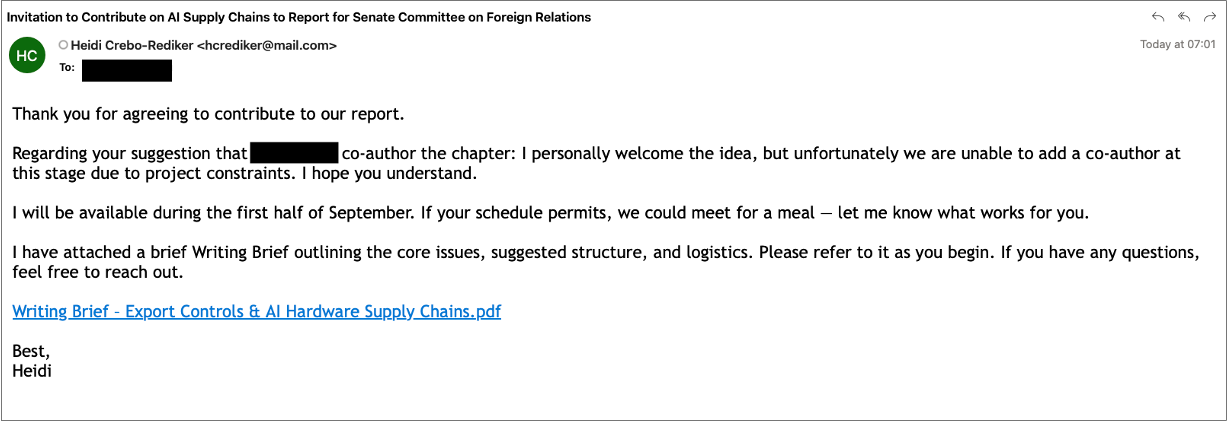
Security firm Proofpoint has reported that hackers suspected of ties to China attempted to compromise US-based AI-related accounts by impersonating a former White House official and other high-profile figures.
According to Proofpoint, the attackers used fake identities — including that of a former White House bureaucrat — in an effort to steal accounts belonging to individuals and organizations in the US AI field. The firm characterized the activity as an influence or credential-harvesting operation, though the company itself framed the China linkage as an allegation ("의혹," or suspicion) rather than a confirmed attribution.
Proofpoint published supporting material alongside its report, including images drawn from the original findings, which the review preserved via archived copies of the proofpoint.com source pages.
The group's suspected connection to China rests on the security firm's assessment; the report itself labels the tie as a suspicion rather than an established fact. No additional details about the number of targets, success rate, or specific victims were provided in the available material.
The claim that China-linked hackers impersonated a former White House official and others in attempts to hijack US AI accounts aligns with Proofpoint's report, with the attribution question left open — making the overall picture Mostly True.