'LLM Jacking' Cybercrime Spreads as Attackers Hijack Other People's AI Accounts and Servers
Mostly True
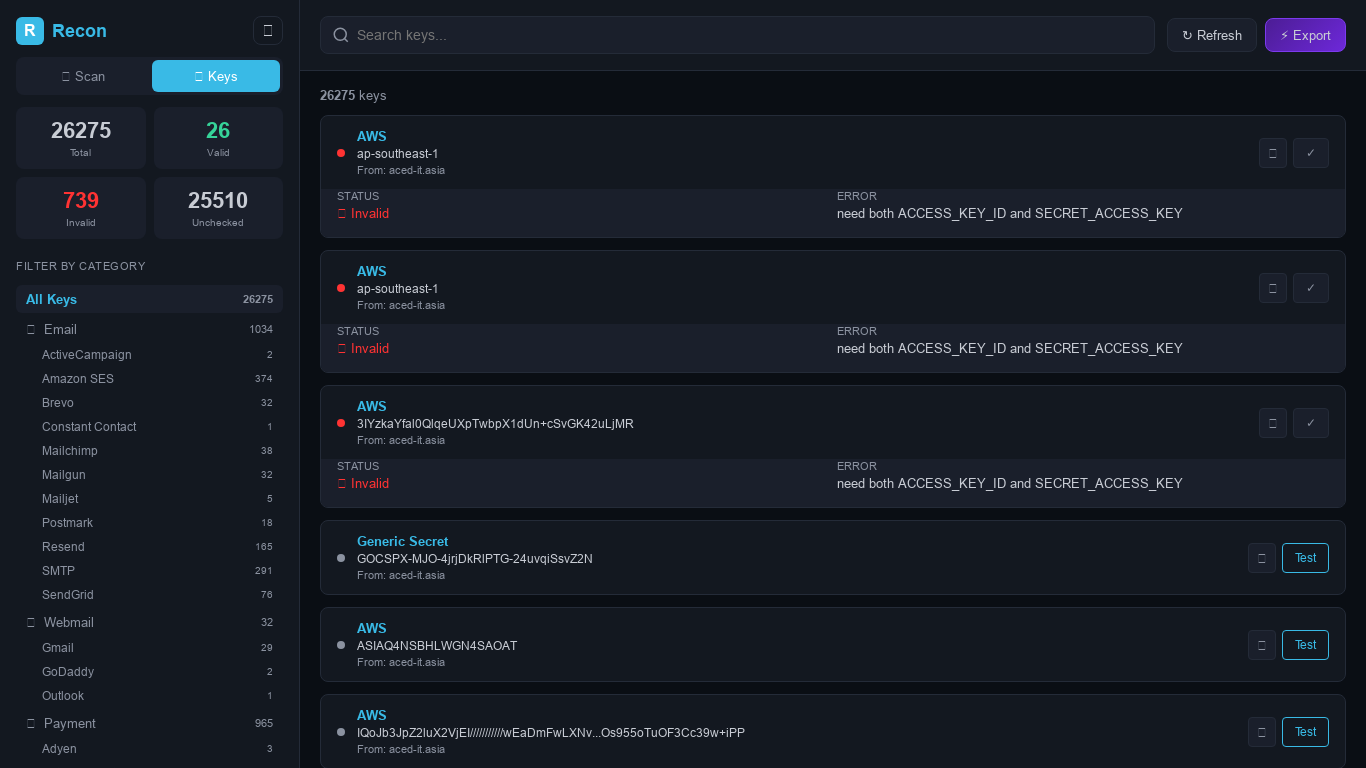
Cybercriminals are increasingly stealing other people's AI accounts and servers to run large language models (LLMs) at someone else's expense, a scheme known as 'LLM jacking.' The practice lets attackers tap paid AI services and computing resources without paying, and it is spreading as generative AI adoption grows.
How the scheme works
LLM jacking typically involves attackers obtaining stolen credentials for cloud or AI service accounts, then using those accounts to access LLM services. In some cases, compromised servers are converted into unauthorized computing resources for running AI workloads. The victims are billed for the usage, while the attackers receive AI capabilities for free.
The scheme is attractive to criminals because legitimate access to powerful LLMs and the GPU infrastructure behind them can be costly, and stolen access effectively transfers that cost to account holders.
Growing risk for account holders
For ordinary users and businesses, an LLM jacking incident can mean unexpected charges, service suspension, and the exposure of data stored in compromised accounts. Security guidance circulated with the reports emphasizes credential protection — strong, unique passwords, multi-factor authentication, and monitoring of usage and billing records — as the main line of defense.
Authorities and security researchers note that the scale of the problem is still unfolding, and the full extent of LLM jacking incidents remains unclear as attacks often go undetected until charges appear.
A security challenge tied to the AI boom
The rise of LLM jacking underscores a broader point: as AI services become a standard business tool, the accounts and servers that power them have become targets in their own right, much like cloud infrastructure before them. Companies offering AI services face pressure to harden authentication and detect abnormal usage patterns, while users are urged to treat AI accounts with the same care as financial ones.
The claim that criminals are hijacking other people's AI accounts and servers to exploit LLMs holds up against the available evidence, with some details about scale and frequency still uncertain — making it Mostly True.
Verdict: Mostly True
- https://v.daum.net/v/20260929003217182
- https://www.sysdig.com/blog/llmjacking-stolen-cloud-credentials-used-in-new-ai-attack
- https://cloud.google.com/blog/topics/threat-intelligence/from-prompting-to-autonomy-the-evolution-of-adversarial-ai/
- https://securityledger.com/2026/09/google-llmjacking-powers-cybercriminals-use-of-ai/
- https://www.anthropic.com/threat-intelligence-report-september-2026
- https://www.pillar.security/blog/operation-bizarre-bazaar-first-attributed-llmjacking-campaign-with-commercial-marketplace-monetization
- https://labs.cloudsecurityalliance.org/research/csa-research-note-llmjacking-offensive-ai-tooling-20260618-c/
- https://biz.chosun.com/en/en-it/2026/09/28/MZKBJSNQO5DRTBC7VL4KOKU6CM/
- https://www.bleepingcomputer.com/news/security/80-000-plus-organizations-had-ai-logins-stolen-from-shadow-ai-to-llmjacking/
- https://www.ft.com/content/3f406fbe-b72e-488f-9975-5b94e95dfe32
- https://storage.googleapis.com/gweb-cloudblog-publish/images/Figure_3_Recon_dashboard.max-1400x1400.png
- https://storage.googleapis.com/gweb-cloudblog-publish/images/Figure_6_Threat_actors_are_leveraging_AI_a.max-1500x1500.png
