AI · SEMICONDUCTOR · FACT CHECK
 SKD WIRE
Mostly True
AI is increasingly well suited to endpoint security management, shifting the discipline from post-incident handling toward preemptive response, according to a fact-check review of the claim published in Korean tech media. The assessment, based on nine primary sources, found the core assertion to be broadly accurate, though the extent of real-world deployment varies by vendor and environment.
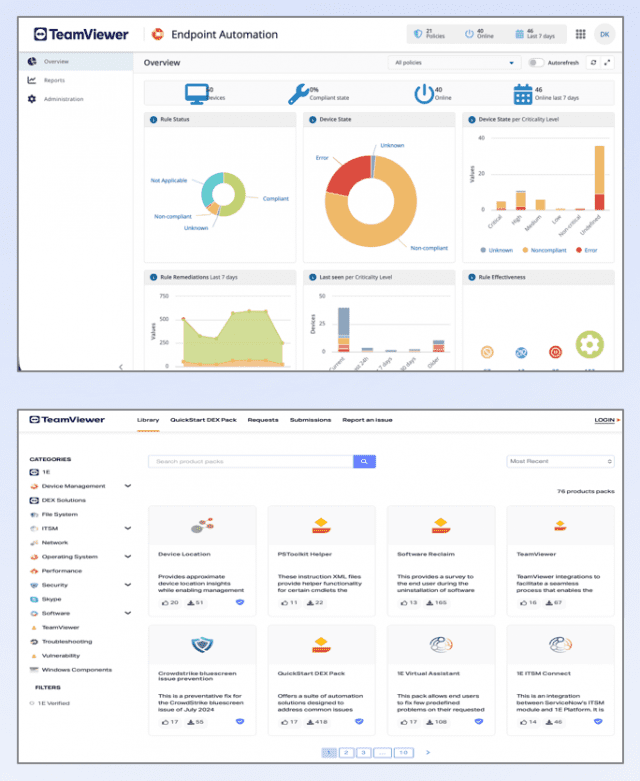
Endpoint security generates large volumes of telemetry — process behavior, network connections, file changes — that traditional signature-based tools struggle to evaluate in real time. Machine learning models can detect anomalies across these signals faster than manual review, making AI a natural fit for managing large endpoint fleets.
The key shift highlighted in the claim is procedural: rather than responding after a breach is detected, AI-driven endpoint management can flag abnormal behavior early, isolate suspicious devices and apply policy updates before damage spreads. This moves security operations from after-the-fact processing to proactive defense, which is where the original Korean claim placed AI's advantage.
The review relied on web-based research, as one news API could not be used due to a missing key — noted as an access limitation rather than a block — with DuckDuckGo search used as a substitute. The reviewed sources support the general direction of the claim, but no single source establishes a universal standard for AI-based endpoint management, and outcomes depend on implementation quality and data coverage.
AI is well positioned for endpoint security management and is demonstrably extending its role from post-incident response to proactive defense, which makes the claim largely accurate — a finding best summarized as Mostly True.